How to automate access reviews for SOC 2 compliance
Published
To automate access reviews for SOC 2 compliance, use one platform for the reviews and for the access lifecycle behind them. Serval does both. Its user access reviews assign reviewers to certify or deny every grant in scope and export each decision as audit evidence. Its access management logs every request, approval, provisioning step, and revocation. The auditor asks for evidence; you export it.
SOC 2 Type II access review requirements trip up many IT and security teams not because the requirements are ambiguous, but because the evidence collection process is painful. Pulling a list of who has access to what, matching it against who should have access, documenting approvals, and showing that temporary access was actually revoked, done manually, this takes weeks. Done once. Then you do it again next quarter.
This guide covers what SOC 2 actually requires for access reviews, why manual processes fail at scale, and how to set up automation that produces compliant evidence as a natural output.
What does SOC 2 require for access reviews?
SOC 2 Type II is an audit of operating effectiveness over a defined period. For access controls, the auditor is evaluating whether your stated policies match what actually happened over time. The relevant controls fall into three areas.
Access is granted based on policies. The auditor wants to see that access decisions follow defined rules, not ad hoc approvals or informal resolutions. Access policies should specify who can request what, what approval is required, and what duration limits apply. The audit evidence should show that requests followed those policies consistently.
Access is reviewed regularly. Periodic access reviews demonstrate that you are not accumulating stale permissions. The standard does not specify a frequency for all roles, but admin and privileged access is typically expected quarterly or more frequently. The evidence is a record of who had access, when it was reviewed, and what happened as a result: revocations, confirmations, or flags for follow-up.
Access is removed when no longer needed. Deprovisioning is one of the most frequently cited failure points in SOC 2 audits. An employee changes roles or leaves the company, and their access lingers. The evidence the auditor wants to see: that access was revoked, when it was revoked, and that the revocation was systematic rather than relying on a human to remember.
Together AI automates 95% of just-in-time access requests through Serval. Todd Thiel, Senior Manager of Enterprise Security at Together AI, puts it this way: "Serval is performing all of the authorization logic for granting access to infrastructure, and it's doing it in a transparent way." Transparent is the operative word for SOC 2.
Why manual access reviews fail at scale
The manual access review process has a structural problem: the evidence collection burden grows with the number of applications, roles, and users. For a 50-person company with five applications, a manual quarterly review is manageable. At a Fortune 500 company with hundreds of applications and reviewers, the same review takes weeks of spreadsheets and follow-ups, and the output is only as accurate as the last export from each system.
Three failure modes are common:
Stale access accumulates undetected. Without automatic deprovisioning, employees who change roles or leave the company retain access until someone manually removes it. Access reviews are supposed to catch this, but if the review itself is a manual process, stale access accumulates between reviews.
Approval chains are not documented. In a manual process, approvals happen over email or Slack messages. By audit time, those records may be scattered, deleted, or inaccessible. Auditors want a structured record of who approved what and when.
Access duration is not enforced. If an employee is granted temporary access to a production environment for a specific project, and that access is not automatically revoked when the project ends, "temporary" becomes indefinite. Auditors ask for evidence of revocation; the evidence is not there.
Automation closes each of these failure modes by making the audit trail a structural output of the access workflow, not a separate documentation exercise.
How to automate SOC 2 access reviews with Serval
Serval manages the complete access request lifecycle: request, eligibility check, approval, provisioning, active access, and automatic revocation. The audit trail is generated at every step.
Step 1: Connect your identity provider and applications
Serval integrates with your identity provider (Okta, Microsoft Entra ID, JumpCloud) and imports existing roles, groups, and policies. When you connect an application, you define the API scope, what Serval can ever access, not just what it uses today. That ceiling is set once and cannot be exceeded by any workflow.
Connecting the IdP also establishes the source of truth for who employees are and what their current role attributes are. Access policies evaluate requests against live IdP data, not against what the AI infers from the message.
Step 2: Configure access policies for each role
For each application role, configure an access policy that specifies: who can request access (access profiles define eligibility), what approval is required (individual approver, manager, security team, sequential chain), what duration limits apply (hours, days, weeks, or months, with a recommended default), and whether a business justification is required.
Serval supports multiple approval steps in sequence: requiring manager approval followed by security team approval for production access, for example. These are hard-coded into the policy. The workflow enforces them the same way for every request. The approval chain is logged: who was asked, what they decided, and when.
For roles with elevated risk, admin access, production systems, financial applications, configure shorter maximum durations and require business justification. For standard business application access, configure longer durations with manager approval only.
Step 3: Set up automatic deprovisioning
Access policies in Serval set a maximum duration for each role, from hours to months or indefinite. When you approve access for a defined duration, Serval sets an expiration. When the expiration hits, Serval removes access using the same provisioning method that granted it, no human needs to remember. The deprovisioning event is logged with a timestamp and reason, such as a scheduled expiry or a manual revocation.
For audit purposes, the log shows the full lifecycle: when access was requested, when it was granted, who approved it, and when it was revoked. A SOC 2 auditor asking “prove that this user’s temporary access was removed” gets an exportable record of when it was requested, provisioned, and removed.
Step 4: Run user access reviews
Serval’s user access reviews handle the periodic certification SOC 2 asks for. Scope a review by team, application, role, or tag, and Serval snapshots every grant in scope and assigns reviewers from your review policy, including multi-step reviewer chains. Reviewers certify, deny, or skip each grant and get reminders in Slack, Microsoft Teams, and email. Optional AI insights suggest a decision for each grant from its request history, last sign-in, and peer access, and the audit trail marks every accepted suggestion. When the review closes, the owner revokes denied access in one remediation step.
For evidence between reviews, scheduled workflows built with Catalyst can send a weekly admin access report or flag contractors whose access expires within 7 days.
Step 5: Export audit evidence when your auditor asks
Each user access review exports as an XLSX workbook (summary, resources in scope, the per-grant decision matrix, and revocations) or as a CSV decision matrix. Each role’s request log exports as CSV with the user’s email, the ticket ID, and timestamps for when access was requested, provisioned, deprovisioned, and set to expire. Org admins can also export the organization audit log of every access grant and deprovisioning.
Best practices for ongoing access governance
Review sensitive access frequently, standard access quarterly. Admin and production access should be reviewed monthly at minimum. Standard application access can be reviewed quarterly. Serval's scheduled workflows make the review cadence automatic rather than dependent on someone scheduling a review.
Use time-bound access as the default, not the exception. Permanent access is harder to audit and harder to remediate when something goes wrong. For most roles, time-bound JIT access with automatic deprovisioning is the right model. Build extension workflows for cases where continued access is genuinely needed.
Keep the policy configuration in sync with your IdP. When you add a new application or create a new role in your identity provider, configure the corresponding access policy in Serval before the first request arrives. Reactive policy-setting, after employees start requesting access, creates gaps in your evidence record.
Document your review cadence. Serval records every review and decision, and the SOC 2 auditor also wants to see a defined process behind them. Write down the cadence, who is responsible for reviewing the output, and what constitutes a finding that requires action.
Frequently asked questions
How do Fortune 500 companies automate access reviews for compliance audits?
Large enterprises automate access reviews by snapshotting every grant in scope, routing each one to the right reviewer, and exporting the decisions as evidence. Serval’s user access reviews do this across teams and applications: review policies assign reviewers in steps, reminders go out in Slack, Teams, and email, optional AI insights suggest certify or revoke, and the XLSX report holds the per-grant decision matrix and revocations for SOC 2 audits.
Which tools automate access reviews and produce exportable audit evidence?
Serval runs user access reviews where reviewers certify or deny each grant, then exports the results as an XLSX workbook or CSV decision matrix. Its access management also exports each role’s request log as CSV with the user’s email, ticket ID, and request, provisioning, deprovisioning, and expiry timestamps, and scheduled workflows can send recurring access reports to the security team.
How do you prove automatic deprovisioning to a SOC 2 auditor?
Serval logs every deprovisioning event with a timestamp and reason, such as a scheduled expiry or a manual revocation. The deprovisioning record appears in the same audit log as the original access grant, providing a complete lifecycle view: who requested access, who approved it, when it was provisioned, and when and why it was revoked. The request, provisioning, and deprovisioning timestamps export as CSV for compliance evidence.
How do you handle access reviews for contractors and temporary workers?
Serval's access policies support configurable duration limits for each role. For contractor access, configure shorter maximum durations that align with contract periods. Serval's Catalyst Agent supports a weekly contractor expiration review: every Monday, identify contractors whose access expires within 7 days and notify managers to confirm or extend. Contractors who leave without renewal have their access revoked automatically when the duration expires, with the revocation logged.
What is the difference between access review automation and access request automation?
Access request automation handles the workflow when an employee requests access: intake, eligibility check, approval routing, provisioning, and deprovisioning. Access review automation is the recurring process of reviewing who has access to what and removing stale or unnecessary permissions. Both are part of a complete SOC 2 access governance program. Serval supports both: the complete JIT request lifecycle for individual access requests, and user access reviews for periodic certification.
You may also be interested in

Sam Stewart joins Serval as Head of Security
Sam Stewart will lead security at Serval as its AI agents take on more of the enterprise's most sensitive work.
Company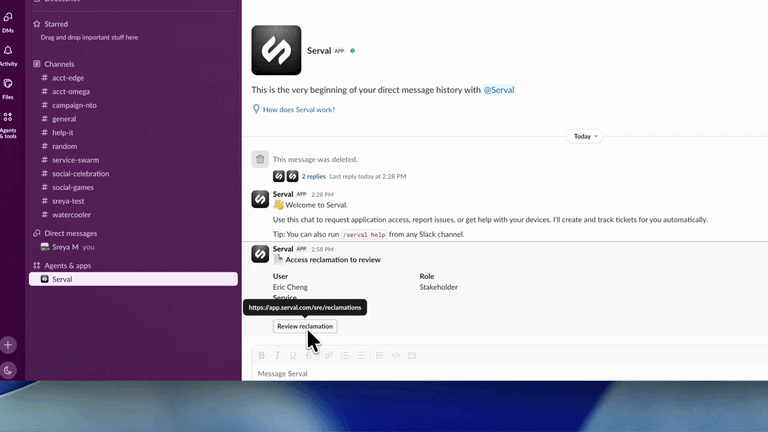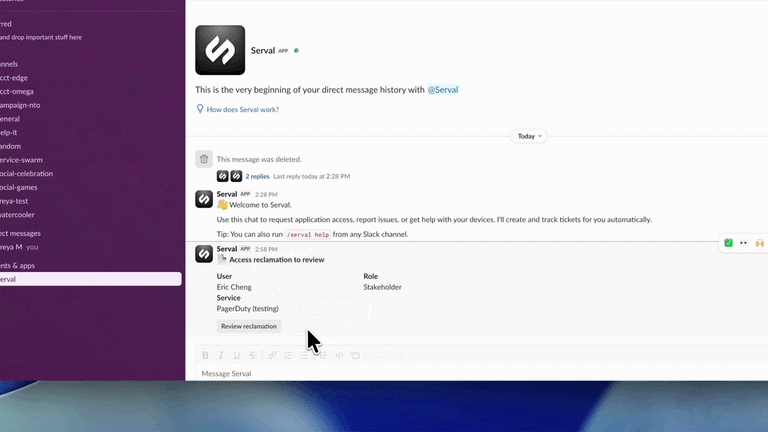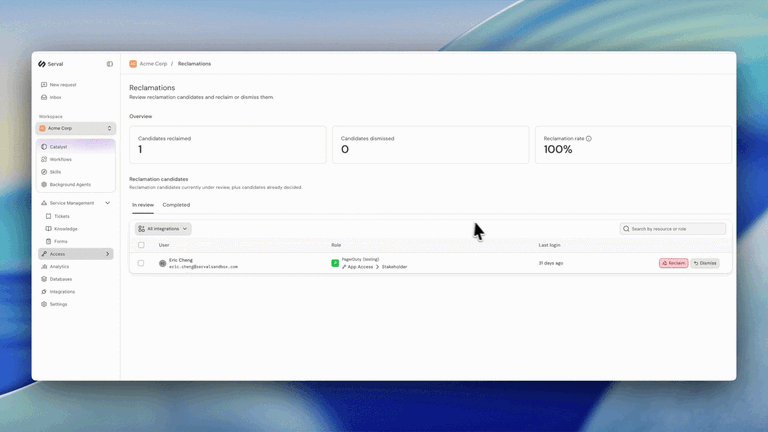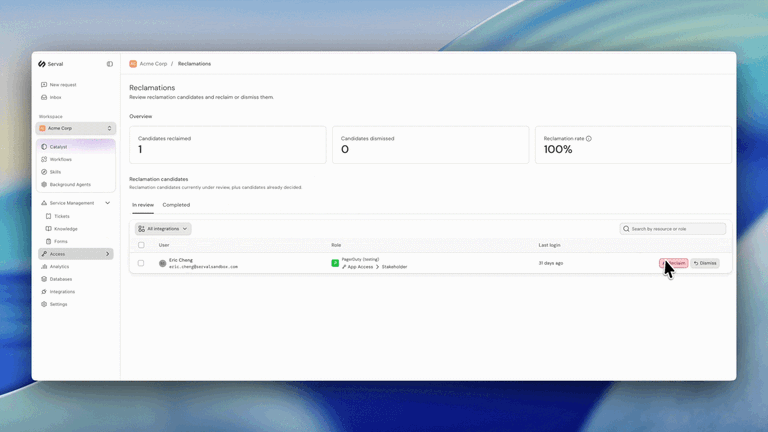
Introducing automated license reclamation
Serval reclaims seats as they go unused, on a policy you set once.
Product
Announcing general availability of Catalyst
Today, we're excited to announce that Catalyst is generally available and will be enabled by default for all organizations.
Product